A card transaction happens in Colombo. The customer’s registered mobile device appears hundreds of kilometres away.
That mismatch does not prove fraud. But it gives the bank another useful signal before approving the transaction.
This is where device location verification turns telecom location intelligence into a service banks can use.
Card Fraud Needs More Than OTPs
Banks already use OTPs, device fingerprinting, transaction history and behavioural analytics. Fraudsters continue to adapt.
UK Finance reported that remote purchase card fraud reached £423.5 million in losses across 3.2 million cases in its 2026 fraud report. (ukfinance.org.uk)
Location verification adds another question to the fraud decision:
Is the customer’s mobile device actually near the location associated with this transaction?
The answer should not replace existing fraud controls. It should strengthen them.
What Is a Device Location Verification API?
Instead of giving a bank a customer’s exact location, the operator can expose an API that answers a narrower question:
Is this device inside a requested geographic area?
The CAMARA Location Verification API is designed around this model. An application provides a geographic area, and the mobile network checks whether the device is within it. (camaraproject.org)
The result can then be used as another input in the bank’s fraud decision.
This is important because the operator keeps control of the underlying location data instead of exposing raw subscriber coordinates directly to every enterprise application.
A Simple Banking Example
Imagine a customer uses a card at an ATM in Kandy.
Before approving a high-risk withdrawal, the bank sends a request through the location API gateway.
The request could contain the customer’s authorised device, the ATM area and a requirement for sufficiently recent location information.
If the network confirms the device is near the ATM, that becomes a positive risk signal.
If the network indicates the device is far outside the expected area, the bank can increase the transaction’s risk score or request additional verification.
CAMARA specifically identifies banking fraud prevention as a Location Verification use case, including checking whether a device is near an ATM or card transaction location. (camaraproject.org)
Location should still be treated as one signal rather than an automatic reason to block a transaction. A customer may leave their phone behind, carry multiple devices or use more than one SIM.
Why Telcos Have a Valuable Signal
A banking app can request GPS information from a device.
But network-derived location gives the bank another source of evidence.
The operator already has network infrastructure capable of determining or estimating the location of connected devices. A standardized API allows that capability to be offered to approved enterprise customers without forcing them to understand telecom network infrastructure.
CAMARA also lists comparison against device-reported GPS information as a potential use case for Location Verification. (open-gateway.gsma.com)
That makes network location useful when an enterprise wants an additional signal beyond information coming directly from the device.
How This Fits hSenid LBS
The hSenid LBS material shows a similar separation between enterprise applications and the telecom network.
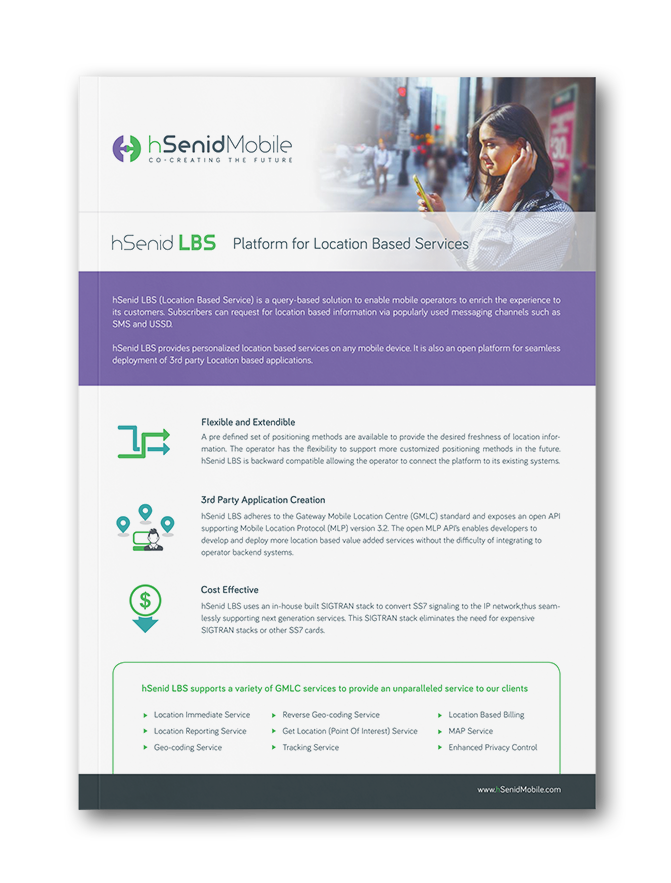
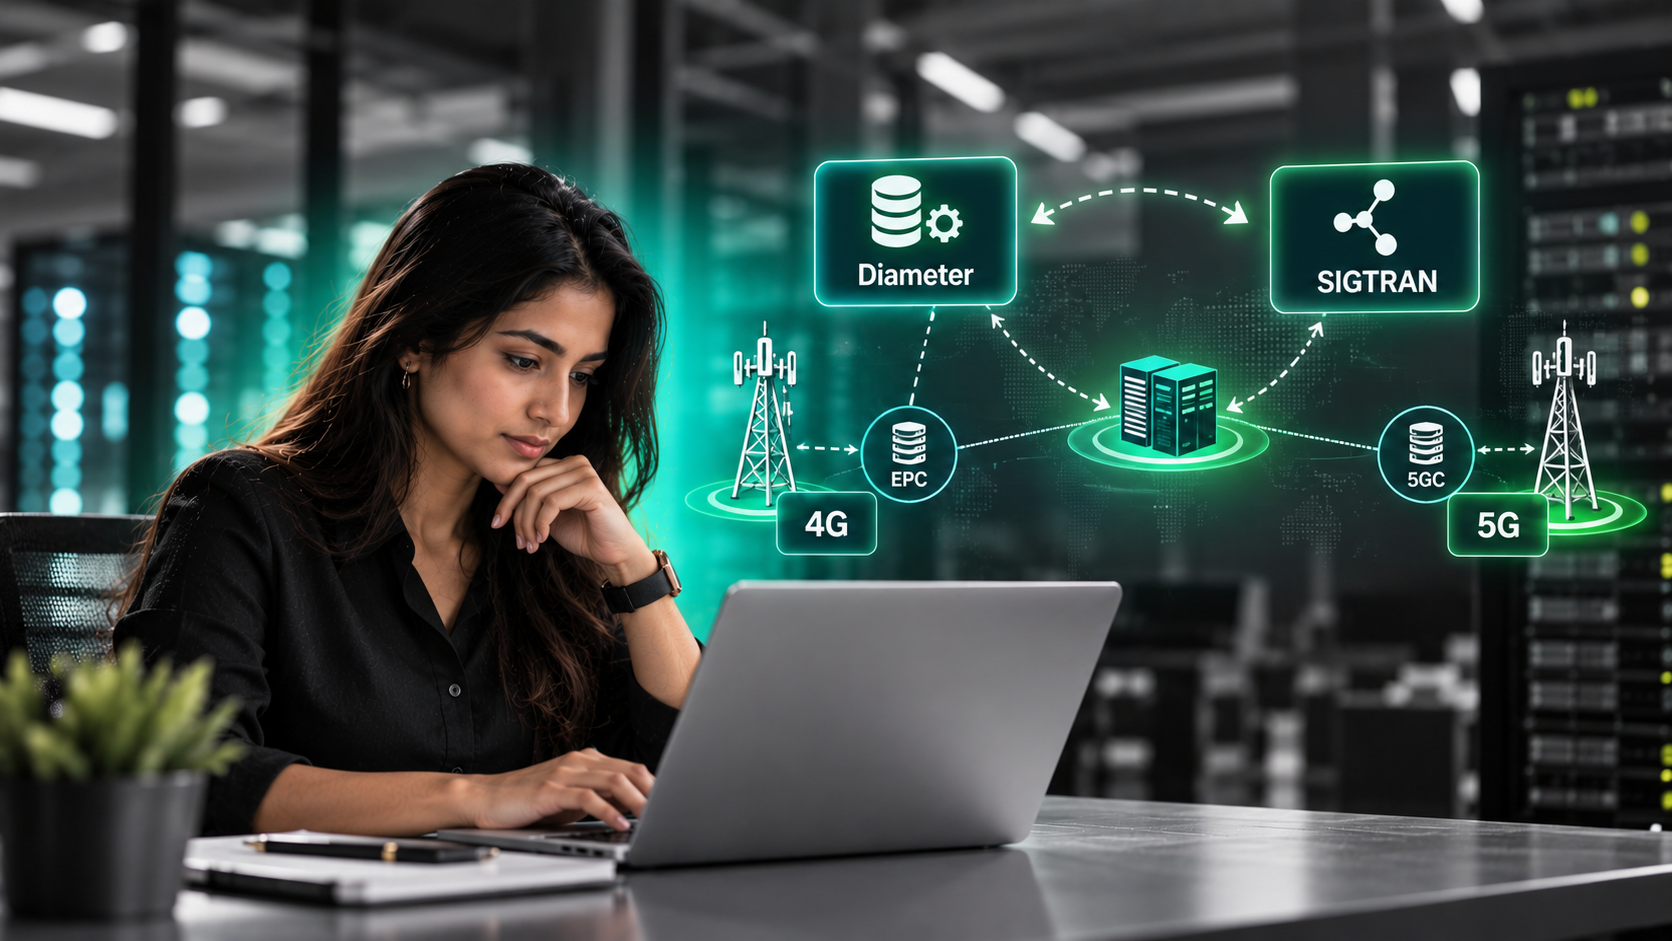
Third-party applications connect through an MLP interface, while the platform handles positioning methods including ATI, PSI, SIGTRAN and customised positioning methods.
That separation is useful for banks.
A bank should not need to integrate directly with every underlying positioning method. It should call a controlled location service while the operator manages the network complexity underneath.
The hSenid LBS material also lists services including location reporting, tracking, geocoding, reverse geocoding, location-based billing and Enhanced Privacy Control.
This provides a base for exposing location capabilities as enterprise services instead of building separate integrations for every customer.
What Operators Need to Productize
Exposing location is only the technical starting point.
A commercial device location verification service also needs authentication, enterprise onboarding, privacy controls, consent where required, API monitoring, audit logs and a charging model.
Location freshness matters too.
CAMARA allows applications to specify how recent the location information should be. If recent enough data is not available, the service can return an error instead of relying on stale information. (open-gateway.gsma.com)
For a fraud system making decisions in seconds, that matters.
From Network Capability to API Revenue
Operators already have network signals that can be valuable to banks and fintechs.
The opportunity is to turn those capabilities into controlled enterprise APIs.
A bank does not need continuous access to a customer’s movements. It may simply need one answer at one important moment:
Does the network location support where this transaction says the customer is?
A location API gateway can make that possible while keeping privacy, network integration and access control with the operator.
For telcos, device location verification creates a practical way to turn location intelligence into a commercial API for banking, fintech and other fraud-sensitive industries.