SMS is still a major revenue channel for telecom operators.
Juniper Research estimated operator business messaging revenue at $51.7 billion in 2025. But when A2P messages reach subscribers through unauthorized routes, operators can lose the revenue they should have earned from that traffic.
That is the grey-route problem.
For operators, fixing it is not only about detecting fraud. It is about knowing where enterprise traffic enters the network, controlling how it is routed, charging it correctly and maintaining visibility across the entire messaging flow.
What is grey route SMS?
A grey route is an unofficial path used to deliver SMS traffic while avoiding the intended commercial A2P route.
For example, a business may send an OTP, banking alert or promotional message through a messaging provider. Instead of entering the destination network through an approved A2P connection, the traffic may be redirected or disguised as another type of messaging traffic.
In some cases, business-generated traffic can appear similar to lower-value P2P messaging.
The customer may still receive the message.
That is what makes grey routes difficult to identify from delivery statistics alone. The message was delivered, but the operator may not have received the expected A2P termination revenue.
Why grey routes matter at scale
The problem becomes significant when messaging volumes grow.
Juniper Research projected that SMS firewalls could prevent more than $4.4 billion in lost business messaging revenue between 2023 and 2027. It also projected grey-route usage in business messaging to decline as more operators deploy stronger traffic controls.
At hSenid Mobile, our systems handle nearly 50 million transactions daily.
At this kind of scale, even a small amount of incorrectly routed traffic can become commercially meaningful.
Operators therefore need visibility into where traffic originates, how it enters the network and what commercial rules should apply to it.
Start with an SMS firewall
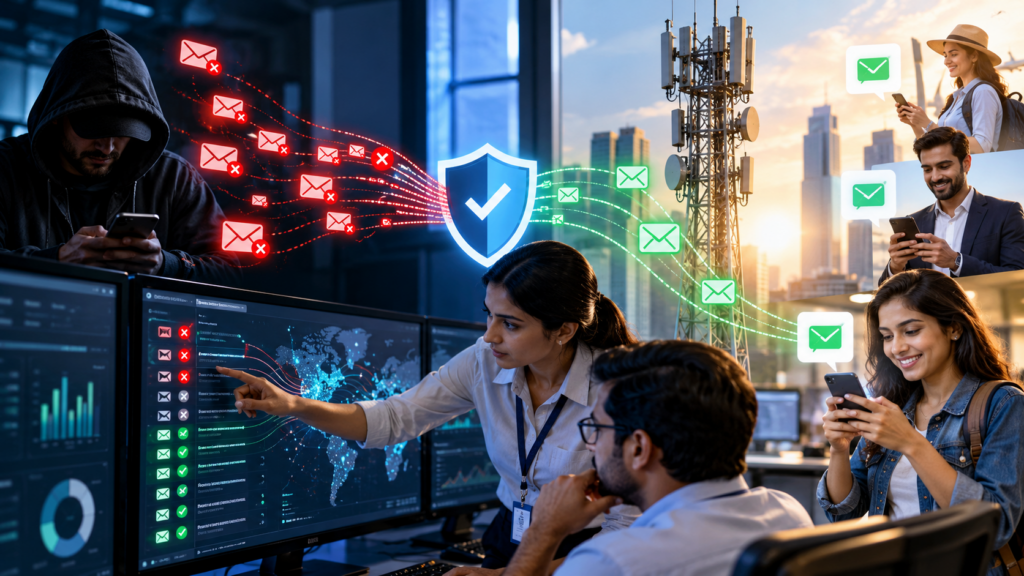
An SMS firewall is one of the main tools operators use to identify suspicious messaging traffic.
It sits at the network boundary and examines incoming SMS traffic before allowing it deeper into the messaging infrastructure.
The objective is straightforward: identify traffic that does not match the expected route or messaging type.
This can include business traffic attempting to use unauthorized routes, suspicious sender patterns, spoofing or traffic originating from unexpected sources.
Once identified, the operator can block, redirect or investigate that traffic.
But the firewall is only one part of the architecture.
The SMSC controls what happens next
Once legitimate traffic enters the network, the SMSC determines how that traffic is processed.
This is important because operators may receive messaging traffic from multiple enterprise applications, aggregators, partners and other SMSCs.
hSenid SMSC allows routing rules to be configured through a management interface. Actions such as relay and reanalysis can then be applied based on those rules.
Its SMPP Gateway can also connect with multiple SMSCs, perform load balancing and manage traffic from ESMEs and SMPP clients.
Instead of treating every message the same way, operators can apply routing logic based on how the traffic entered the network and where it needs to go.
Charging is part of revenue protection
Stopping grey routes means little if legitimate A2P traffic is not charged correctly.
The SMSC therefore needs to connect messaging activity with the operator’s charging and billing environment.
hSenid SMSC supports both real-time and offline charging for prepaid, postpaid and roaming subscribers. It also produces detailed CDRs in flexible formats for billing purposes.
The flow becomes simple:
Identify the traffic → apply the correct routing rule → charge it → record it.
That gives operators a clearer connection between network activity and commercial revenue.
Traffic spikes should not become revenue leaks
A2P traffic can change quickly.
OTP campaigns, banking notifications, enterprise alerts and promotional campaigns can create sudden increases in message volume.
If the infrastructure cannot handle those peaks, legitimate paid traffic may be delayed or lost.
hSenid SMSC includes overload protection. When traffic exceeds the configured Message Delivery Attempt level, excess capacity can be buffered and delivered afterward.
Revenue assurance therefore is not only about blocking unauthorized traffic.
It is also about making sure legitimate traffic is successfully processed.
Make every A2P message accountable
Grey routes become a commercial problem when operators cannot clearly see how messaging traffic is entering and moving through their network.
The practical goal is to answer a few questions for every message:
Where did it come from?
Was it using an approved route?
Which routing rule was applied?
Was it charged correctly?
Was the transaction recorded?
Combining an SMS firewall with a scalable SMSC gives operators greater control over those decisions.
Grey routes take advantage of gaps in visibility.
Protecting A2P SMS revenue starts by closing those gaps.