A sudden increase in OTP traffic can look positive on a dashboard.
More messages. More transactions. More traffic through the network.
But what if thousands of those OTPs were triggered by bots rather than real customers?
That is the problem with SMS pumping, also known as Artificially Inflated Traffic (AIT).
Juniper Research describes AIT as non-genuine A2P SMS traffic deliberately generated to increase messaging volumes and create unnecessary costs for enterprises. It has become one of the most prominent fraud tactics in mobile messaging.
For operators, this is not simply a fraud problem. It can damage the economics and credibility of the entire A2P ecosystem.
What is SMS pumping?
SMS pumping usually starts with a legitimate service.
Consider an enterprise login page that sends an OTP whenever somebody enters a phone number.
A fraudster automates that process.
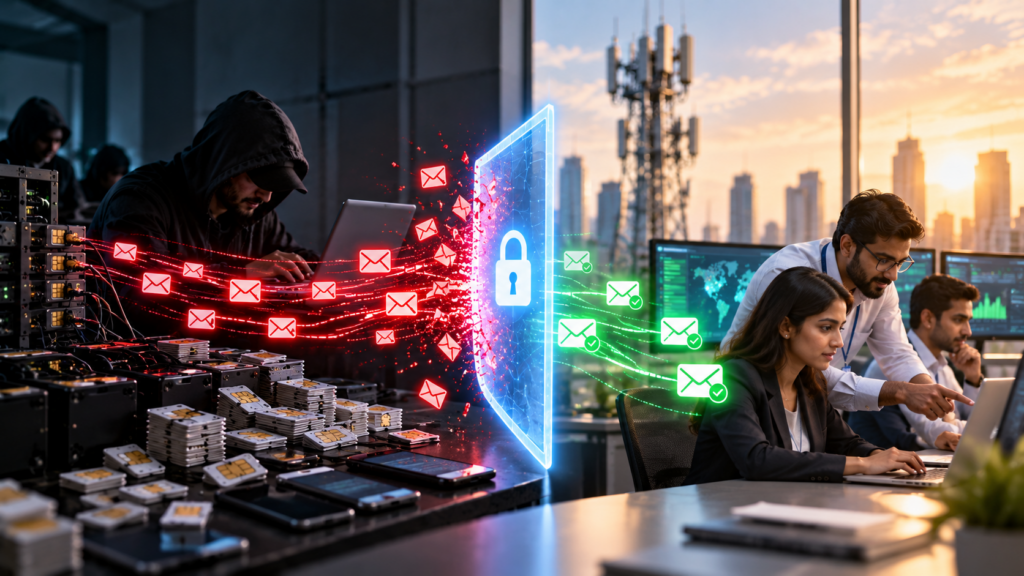
Bots create fake accounts or repeatedly request verification codes. Each request triggers a real A2P SMS, even though there is no genuine customer behind it.
Juniper Research describes cases where fraudsters work with another party that benefits financially from the resulting messaging traffic. The process can then be repeated at scale, particularly where international SMS delivery costs are high.
To the network, the messages can initially look legitimate.
They are real OTPs generated by a real enterprise.
The problem is that the demand behind them is fake.
The numbers show why operators should care
Juniper Research found that enterprise losses from AIT peaked at $2.1 billion in 2023. Its research projects those losses to fall by 55% between 2024 and 2029 as enterprises and messaging providers strengthen their defenses and some authentication traffic moves to other channels.
Juniper also identified the decline of AIT as its number-one telecom trend for 2025, forecasting an 8% reduction in global enterprise losses during that year as SMS firewalls and other controls improve.
But there is another cost that is harder to put on a dashboard: trust.
If an enterprise repeatedly pays for OTPs that never correspond to genuine users, SMS starts looking expensive and inefficient.
That matters to operators because A2P SMS remains a large business. Juniper Research estimates operator business messaging revenue at $51.7 billion in 2025.
Protecting that market means making sure enterprises can trust the traffic they are paying for.
What AIT can look like in real traffic
AIT detection is difficult because a fraudulent OTP may look almost identical to a legitimate one.
The signal often comes from behaviour rather than the individual message.
A sharp rise in OTP requests from one application, unusually high traffic toward particular destinations, repeated requests from the same source, or large messaging volumes without corresponding successful registrations can all justify investigation.
Juniper specifically points to monitoring large volumes of randomized messages and OTP conversion rates, limiting repeated SMS requests from the same IP address and using bot-blocking tools as protective measures.
The important point is simple: message volume alone is not proof of customer demand.
Operators and enterprises need context around that volume.
Where the SMS firewall fits
SMS firewalls help operators inspect traffic and identify patterns that do not match normal messaging behaviour.
As attackers become better at making artificial traffic resemble legitimate OTP traffic, static rules alone become less effective.
Juniper notes that AIT has historically been difficult for firewalls to detect because the SMS itself can be indistinguishable from legitimate authentication traffic before reaching the destination number.
That makes behavioural monitoring, traffic history and collaboration between operators and enterprises increasingly important.
But detecting suspicious traffic is only one side of the problem.
Operators still need control over what happens to legitimate traffic.
The SMSC provides the control layer
At hSenid Mobile, this matters at real network scale.
Our systems handle nearly 50 million transactions daily.
At that volume, traffic needs to be routed, controlled and recorded systematically.
hSenid SMSC allows operators to configure routing rules through a management interface and apply actions such as relay and reanalysis according to those rules.
Its SMPP Gateway can connect with multiple SMSCs, handle load balancing and manage traffic coming from ESMEs and SMPP clients.
Charging is also part of that control. hSenid SMSC supports real-time and offline charging for prepaid, postpaid and roaming subscribers while generating detailed CDRs for billing.
These capabilities do not replace an SMS firewall or enterprise-side anti-bot controls. They provide the messaging infrastructure needed to manage legitimate traffic once operators know what should be allowed through.
Protect the value behind the message
AIT creates a dangerous illusion.
Traffic increases, but genuine customer activity does not.
For an enterprise, that means paying for interactions that never happened. For an operator, persistent fraud can weaken enterprise confidence in SMS and push authentication traffic toward alternative channels.
The goal should not be maximum SMS volume.
It should be legitimate, accountable and monetizable traffic.
That requires cooperation across the enterprise application, fraud-detection layer, SMS firewall and SMSC.
When every message can be identified, routed, charged and recorded properly, operators have a stronger foundation for protecting both A2P revenue and enterprise trust.